CI-TDF — Built on OpenTDF, Adapted for Practical Use
· Ralf Ulrich Garbe
 28 August 2026
CI-TDF – Built on OpenTDF,
Adapted for Practical Use
From a strong foundation to a stronger practical format
OpenTDF (Trusted Data Format) provides a strong foundation for the data-centric security required by Zero-Trust ecosystems. OpenTDF is well thought out and provides the right starting point. Building on it, we developed ClassifyIt-TDF (CI-TDF), an open, information-centric format adapted for practical use.
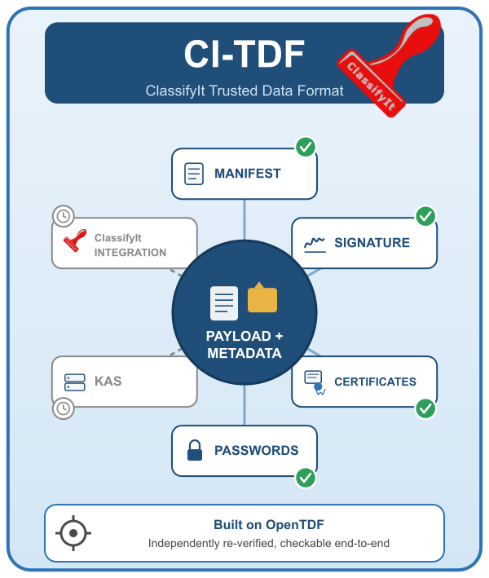
We have developed the first version of the manifest and an application for testing and validating CI-TDF. The test environment lets you encrypt, verify and decrypt files.
The Shared Foundation
Like OpenTDF, every CI-TDF container is a ZIP archive holding a plain, readable JSON manifest alongside an encrypted payload. Nothing hidden, nothing proprietary about the shape - open it, and the manifest reads like any other JSON document.
The Differences
The CI-TDF will be integrated into ClassifyIt and requires some practical adjustments. We added some attributes, like a unique ObjectID for the container, but also the original file's name and size. For practical use, we also support password-based and certificate-based encryption and plan to support a KAS (Key Access Server). In addition, CI-TDF allows for a full metadata file in the container and is designed to support multiple payloads in the future.
What Next
We will continue testing the CI-TDF data structures and consider additional assertions, including classification-marking, access-control and metadata schemas. We intend to integrate CI-TDF into ClassifyIt and add shell extensions to make the format easier to use.
Test It Yourself
ClassifyIt provides a test environment for CI-TDF: a Windows application that creates and opens CI-TDF containers, along with test certificates.
Explore more at: https://classifyit.eu
#ZeroTrust #TDF #ZTDF #OpenTDF #DataSecurity #ClassifyIt #CITDF